Utility Voice AI Operating Model: Converging Outage, Field & Regulatory Workstreams
An operational framework for converging outage communications, validated service‑request intake, and field dispatch inside an account‑safe Voice AI operating model—with governance, resilience and measurable outcomes for utilities.
1. Overview and operating boundaries
Define the scope, high‑level architecture and what Voice AI will—and will not—do. Good operating models start with explicit boundaries and a shared event model for outages, service requests and field work.
Scope and non-negotiable boundaries
Voice AI is an intake, validation and orchestration layer for customer contact. It supports high‑volume requests, initial triage and routing; it does not make safety or engineering decisions, operate field equipment, or substitute emergency response. Establish these boundaries in governance documents, training and procurement terms so vendors and internal teams share expectations.
- Inbound voice and IVR calls are handled for information, status, and validated intake.
- Write operations that impact infrastructure or safety require explicit human authorization.
- Emergency reports escalate immediately to human agents or emergency dispatch—Voice AI only records and routes the intake.
Canonical call flow — canonical architecture
Standardize on a single canonical flow to reduce integration complexity and ensure repeatable controls. At call level: Customer call → Voice AI → account or location validation → approved utility API or knowledge source lookup → service request, status response, or human escalation. Design the Voice AI to use read‑only API calls for status where possible and return structured events to downstream systems.
- Validation first: match account/premise before any personally identifiable information (PII) is disclosed.
- Prefer read‑only queries to OMS/CIS for status; write actions (create ticket, dispatch) go through a controlled adapter with human confirmation.
- Emit standardized events for outage, ticket intake, and escalation for downstream analytics.
2. Core workflows: outage, service intake and field dispatch
Operational success depends on separating workflow intent while sharing identity, event and routing models so outage, billing, service and field teams can act from a single source of truth.
Outage communications: fast, accurate, account‑safe status
Voice AI must balance speed and accuracy for outage calls. Use pre‑verified location tokens and outage event IDs where available. For status queries, return read‑only data (restored vs active, estimated restoration when published) and avoid inference when system data is absent—prompt for human assistance.
- Map OMS outage IDs to the Voice AI event model to avoid ambiguous responses.
- Use templated responses for confirmed outage states; escalate when data gaps exist.
- Log caller confirmations and consent to record for regulatory or billing disputes.
Validated service‑request intake
Service requests (meter issues, billing inquiries, non‑life‑safety leaks) require structured intake: identity validation, location confirmation, symptom taxonomy, and next‑step routing. Where possible, capture supporting metadata (time, photos via SMS link, prior tickets) and attach to the CIS/CRM ticket.
- Use layered validation: basic voice match, knowledge‑based questions, then an account lookup.
- If verification fails, escalate to an agent rather than creating potentially misattributed tickets.
- Attach voice transcript, event metadata and intent classification to the service request for auditability.
3. Integration patterns and account‑safe validation
Integrations determine both capability and risk. Adopt conservative default patterns—read‑only queries, tokenized identifiers, and escrowed write paths that require human confirmation.
OMS/CIS/CRM integration patterns
Prefer lightweight, well‑defined adapters between Voice AI and core systems. For status and lookup operations use read‑only endpoints or a cached read model. For create/update operations, route through a controlled orchestration layer that enforces schema, business rules and human confirmation.
- Design adapters to emit clear success/failure codes and to reject ambiguous requests.
- Use event‑driven synchronization (change events with reconciliation) rather than synchronous writes when possible to reduce coupling.
- Instrument every adapter with observability and retry policies; record the adapter version in audit logs.
Account and location validation controls
Layered validation reduces misrouting and fraud. Combine caller authentication (account PIN or payment history question), location confirmation (address readback, device GPS where consented) and system lookup. If the confidence threshold is not met, require agent handoff before any write or dispatch action.
- Define confidence thresholds for automated answers vs mandatory human handoff.
- Record confidence scores, questions asked and answers in the event for post‑call QA.
- Where third‑party assistants or conferencing are used, ensure identity handling is consistent with privacy obligations.
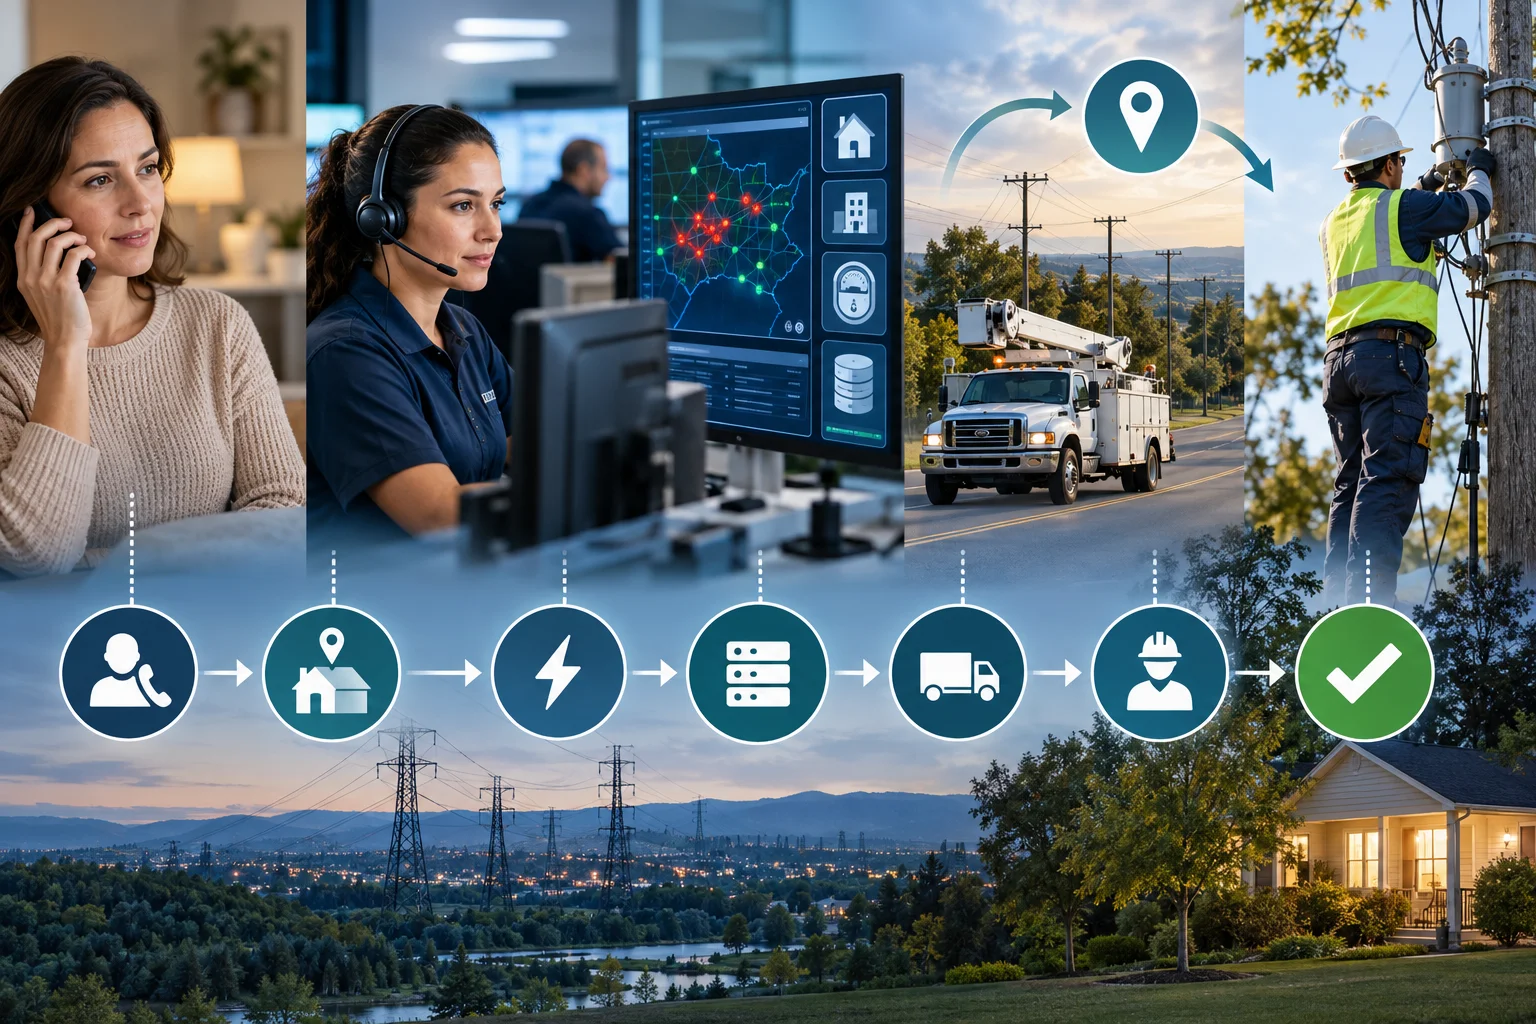
4. Governance, safety controls and human escalation
Governance aligns operational controls, safety boundaries and regulatory readiness. For utilities, this means auditable decision trails, QA, and explicit human‑in‑loop for safety‑adjacent actions.
Human‑in‑loop design and escalation controls
Design explicit handoff points where Voice AI pauses and routes to a human: low confidence, life‑safety indicators, ambiguous account validation, or requests that change service status. Define SLAs for escalation response and decision authority for agents who accept or reject voice‑initiated requests.
- Implement a visible handoff payload for the agent with transcript, confidence, and metadata.
- Set maximum allowable automation for each intent; e.g., automated status replies allowed, service creation requires agent review unless pre‑approved.
- Monitor handoff SLAs and adjust thresholds to balance automation benefits and customer safety.
Audit trails, QA and model governance
Maintain immutable event logs for every call: audio, transcript, intent classification, validation steps, API responses and adapter versions. Use QA sampling aligned to risk (high‑impact intents get higher review rates). Establish model versioning, test datasets, and change control for prompts, scoring thresholds and business rules.
- Store event logs with retention, access control and an index for regulatory requests.
- Sample high‑risk intents (e.g., outages affecting critical customers) more frequently for manual review.
- Record and date‑stamp model and prompt changes; run backtests against historical events.
Safety boundaries and regulated‑workflow enforcement
Explicitly document workflows the Voice AI must never perform unsupervised—such as isolating service to a premise, changing protective settings, or authorizing hazardous work. These are safety boundaries enforced both technically and procedurally.
- Map safety‑critical decisions to human roles and document delegation rules.
- Implement technical guards: read‑only defaults, confirmation tokens, and approval queues.
- Train contact‑centre and field supervisors on Voice AI limitations and escalation paths.
5. Resilience, incident response and operational continuity
Prepare for high‑volume events, integration failures and security incidents. Align incident response playbooks with recognised cyber and operational maturity practices.
Surge capacity, throttling and graceful degradation
Model expected call volumes across seasons and severe weather scenarios. Implement admission control, progressive backoff and degraded modes (status‑only responses, queuing to agents) that preserve core services during peak demand.
- Design a degraded call flow: essential status and escalation paths only when external systems are unavailable.
- Implement adaptive throttling to protect backend systems from cascading failures.
- Advertise temporary self‑service options (SMS status, outage web pages) during large events and record redirects for analytics.
Incident response and continuity controls
Document specific playbooks for integration failures, data corruption, and suspicious activity. Define roles for isolation, forensic collection, notification, and restoration. Align playbooks with cross‑sector cybersecurity and energy sector maturity models where relevant to strengthen coordination between IT, operations and security teams.
- Create separation of duties between platform operations and integration owners to reduce single points of failure.
- Predefine fallback contact lists and hot paths to re‑route calls to agents or alternate providers.
- Maintain encrypted, tamper‑evident logs for post‑incident analysis.
Privacy, data residency and access controls
Document hosting region, backup region, remote‑support access, subprocessors, transfer mechanisms and retention periods. Confirm recording consent and disclosure practices with legal counsel and ensure access controls and audit trails are in place for PII and critical operational data.
- Segregate production audio and transcripts from analytics stores as needed for privacy.
- Define subprocessors and cross‑border data transfer mechanisms and record them in procurement artifacts.
- Require role‑based access with multi‑factor authentication for administrative and support functions.
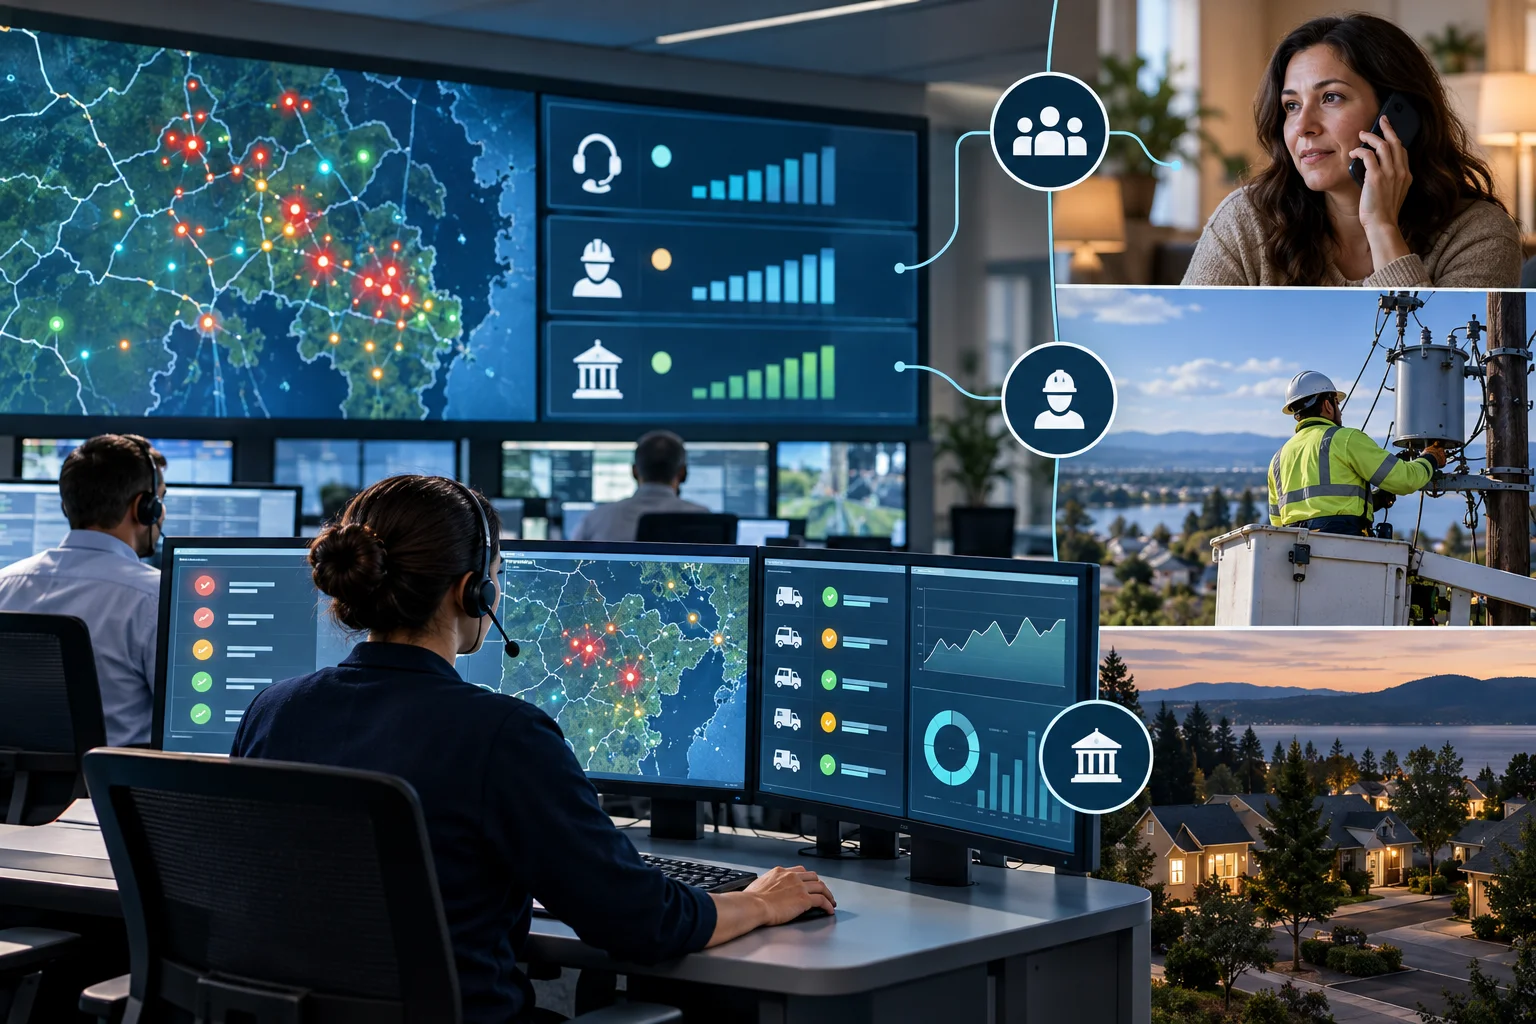
6. Procurement, implementation roadmap and measurable outcomes
Select vendors and plan deployment in phases with clear KPIs, acceptance tests, and accountability for integrations and QA.
Procurement checklist and vendor evaluation
Evaluate suppliers on integration readiness, adapter management, auditability, surge performance, and support for account‑safe validation. Include managed‑service expectations for incident response, logging retention and change control. See Managed Voice AI Services: What Enterprise Buyers Should Expect for a buyer‑oriented checklist and expectations.
- Require a documented adapter inventory and proof of prior integrations with OMS/CIS/CRM systems.
- Request runbooks for surge events and incident response obligations.
- Specify audit logging, retention and export formats as contractual deliverables.
Implementation phases and ownership
Break rollout into three phases: 1) non‑critical automated answers and status lookups; 2) validated intake for service requests with agent handoff; 3) controlled dispatch integration with human confirmation gates. Assign clear ownership for each adapter and operational capability (Contact Centre ops, IT integration, Field Ops, Regulatory Affairs).
- Acceptance criteria per phase: integration test pass, QA pass rate, handoff SLA compliance.
- Run parallel operations and backfilled audits before removing manual paths.
- Keep a rollback plan and freeze windows for model or adapter changes during critical seasons.
KPIs and event‑level analytics
Measure outcomes with operationally meaningful KPIs: verified intake rate, handoff SLA, ticket attribution accuracy, mean time to dispatch for validated requests, false escalation rate, and post‑call QA scores. Instrument event‑level analytics to tie Voice AI events to outage incidents and field completes.
- Track verified intake rate: percentage of calls with successful validation without human assistance.
- Monitor ticket accuracy by sampling and track corrections required after human review.
- Correlate Voice AI event timestamps with OMS outages and field‑completion timestamps for end‑to‑end visibility.
Related Peak Demand resources
Industry and AI sources reviewed
- AI Risk Management Framework — Critical Infrastructure ProfileNational Institute of Standards and Technology (NIST)
- Cross-Sector Cybersecurity Performance GoalsCybersecurity and Infrastructure Security Agency (CISA)
- Cybersecurity Capability Maturity Model (C2M2)U.S. Department of Energy
Utility cybersecurity, critical-infrastructure, records, customer-protection, and emergency-communications obligations vary by jurisdiction and service type. This article is operational guidance, not legal advice; organizations should confirm applicable requirements with qualified professionals.
Frequently asked questions
Use Voice AI to absorb high call volumes, provide approved outage and restoration messaging, validate the caller's account or service location, capture non-emergency service details, and route exceptions to trained staff. It should not estimate restoration times unless those estimates come from an approved utility system of record.
Official reference: Cross-Sector Cybersecurity Performance Goals
The integration design typically depends on the use case, but common systems include the customer information system, outage management system, CRM, knowledge base, notification platform, scheduling tools, and service-request or work-order systems. The Voice AI layer should receive only the data and actions required for the approved workflow.
Official reference: Cybersecurity Capability Maturity Model (C2M2)
No. Voice AI should remain a customer-communication, intake, validation, routing, and escalation layer. Infrastructure control, switching, dispatch authority, emergency response, and safety-critical decisions must remain within approved operational systems and qualified human teams.
Official reference: Cross-Sector Cybersecurity Performance Goals
Ask for evidence of surge and latency testing, account and premise validation, integration failure handling, auditable logs, data minimization, human escalation, change control, incident response, monitoring, and a clear operating model for updates after launch.
Official reference: Cross-Sector Cybersecurity Performance Goals
Build resilient utility customer-service automation
Peak Demand helps utilities connect Voice AI to approved customer-information, outage-communication, service-request, dispatch, escalation, and analytics workflows.
Schedule a discovery call


