Value Realization & Change Architecture for Enterprise Voice AI Programs
A practical buyer and architecture guide for enterprise Voice AI programs. Covers the operational blueprint, managed‑service boundaries, governance, data strategy, procurement checks, and measurable outcomes.
Why a change architecture matters for enterprise Voice AI
Voice AI programs fail to deliver when technology choices are decoupled from operational controls, integrations, and procurement realities. A purpose-built change architecture aligns commercial scope, system boundaries, and measurable outcomes so organizations can scale safely and predictably.
Value realization over point technology
Enterprise buyers should anchor decisions to observable business outcomes (containment, AHT reduction, conversion, SLA compliance) rather than vendor feature lists. That starts with mapping the caller’s intent to an approved downstream system action and identifying where automation changes behaviour, data flows, and compliance obligations. Design decisions—what is automated, what remains human, and what is policy‑gated—determine the program’s ability to deliver repeatable value.
- Map intents to business outcomes before choosing voice models or vendors.
- Identify the smallest safe scope for automation to achieve a measurable KPI.
- Define compensation and recovery actions for failed or partial automation.
Change architecture as an operational contract
Treat the change architecture as a living contract between the business, IT, security, and third‑party providers. It should define ownership for adapters, business‑rules layer logic, orchestration policies, monitoring, incident response, and data lifecycle. This reduces ambiguity during onboarding, upgrades, and incident remediation.
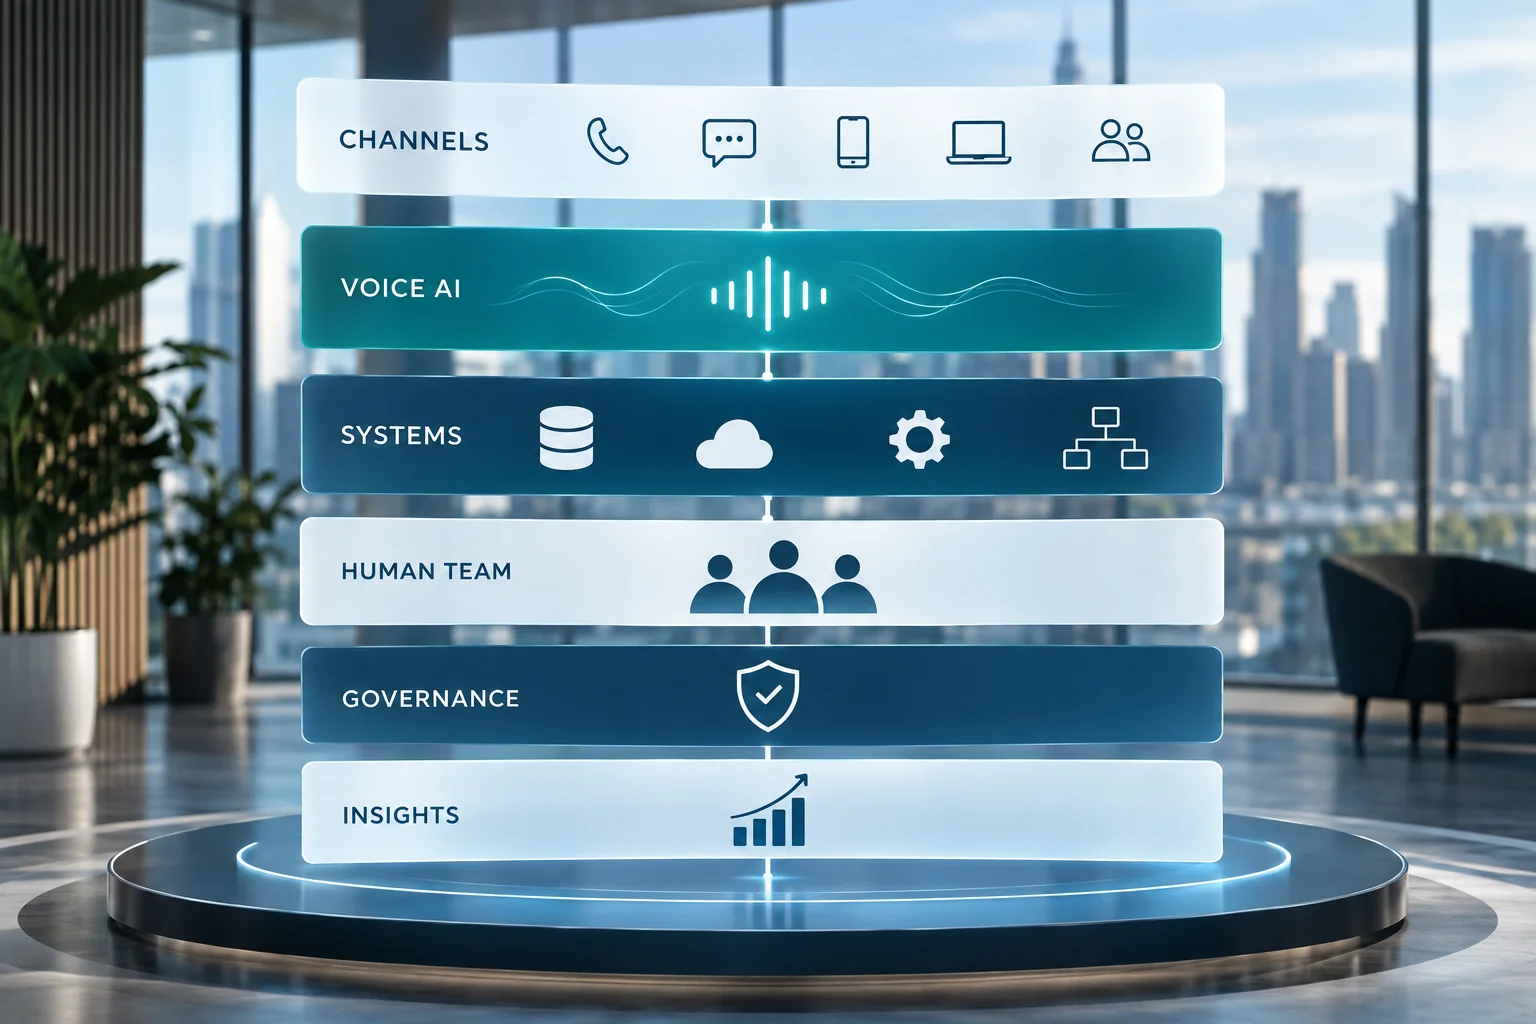
- Use a single canonical diagram that shows Caller → Voice AI → business‑rules layer → approved enterprise systems → response/transaction/human handoff → QA and.
- Include responsibilities for configuration, code, tests, and runbooks in procurement documents.
Blueprint: the caller-to-systems flow and integration motifs
A repeatable blueprint simplifies vendor evaluation, testing, and scaling. The architecture below is intentionally prescriptive about boundaries and integration patterns.
Core flow: Caller → Voice AI → business‑rules layer
At runtime the caller interacts with the Voice AI front end (ASR/NLU/TTS stack, session manager). The Voice AI produces structured intents and entities which are validated and enriched by a business‑rules layer. The business‑rules layer executes deterministic policies (eligibility, entitlement checks, fraud flags) and decides whether to call an enterprise system, return a response, or escalate to a human.
- Keep policy logic out of generative or probabilistic model outputs; use deterministic rules for high‑risk decisions.
- Validate intents with confidence thresholds and allow for multi‑turn confirmation before transactional actions.
- Log decisions and policy inputs for every action to ensure traceability.
Approved enterprise systems and controlled adapters
Integrations to CRM, billing, order management, and case systems must use approved APIs or controlled adapters. Adapters should provide idempotency, transaction compensation for partial failures, and schema validation. Explicit ownership of adapters—who builds, maintains, and secures them—must be contractually defined.
- Require API contracts and test harnesses for each adapter in the SOW.
- Design adapters to fail closed for sensitive writes (e.g., change of billing details) and to provide clear rollback paths.
- Record adapter calls and responses in audit logs with correlation IDs.
Managed service boundaries and operational expectations
When procuring a managed Voice AI service, be explicit about what the vendor manages and what remains with the enterprise. Misaligned expectations are the most common source of contract disputes and operational gaps.
Managed scope and deliverables
A defensible managed‑service scope lists deliverables across infrastructure, integrations, models, orchestration, observability, QA, and human escalation. Expect a vendor to operate the Voice AI stack and provide managed adapters or deliver integration code to the enterprise, depending on the model. For procurement clarity, require a clear table of responsibilities and a rolloff plan.
- Clarify whether the vendor provides adapters or hands over adapter code to the enterprise.
- Define responsibilities for encryption keys, credentials, and identity federation.
- Require runbooks, playbooks, and a documented change‑control process as deliverables.
Service levels, observability and monitoring
Operational SLAs should cover availability, latency, failed session rates, success rates for automated transactions, and observability coverage (traces, metrics, logs). Observability must include end‑to‑end transaction tracing from caller to enterprise system, error categorization, and retention policies for audit data. For architecture guidance on logging and traceability, see Voice AI Audit Logs and Traceability | Peak Demand (https://peakdemand.ca/voice-ai-audit-logs-traceability).
- Specify observability KPIs and required dashboards in the contract.
- Require structured audit logs with correlation IDs, user attributes, and change‑control metadata.
- Define alerting thresholds and incident escalation paths tied to business impact.
Governance, risk management and auditability
Robust governance is not optional for enterprise Voice AI. Risk management identifies where automation increases operational, legal, or reputational risk and prescribes controls to keep high‑risk decisions onshore or human‑gated.
Risk management and policy controls
Implement a continuous risk‑management lifecycle for Voice AI: identify scenarios, assess likelihood and impact, apply mitigation controls, monitor performance, and update policies. Use the NIST AI Risk Management Framework and the Generative AI profile as practical references for integrating risk assessment into design and operations. The OECD AI Principles also support governance constructs like human oversight, accountability, and transparency.
- Classify Action Types (informational, adjudicative, transactional) and apply increasing controls to higher‑risk classes.
- Require human‑in‑the‑loop or human‑on‑the‑loop for decisions affecting legal or financial status.
- Include automated monitoring for drift, bias signals, and anomalous decisioning.
Change control, records, and audit trails
All model, rule, and configuration changes must go through a documented change‑control process with pre‑production validation, approvals, and post‑deployment monitoring. Audit trails should capture who approved a change, test results, rollback triggers, and a timestamped record of production behaviour for at least the retention period required by your policies.
- Version control for rules, prompts, and model configurations with immutable audit logs.
- Approval workflows that include business, security, and legal sign‑offs for policy changes.
- Retention and export capabilities for records to support compliance and forensic investigations.
Operationalizing oversight
Operationalizing human oversight requires concrete workflows that connect business rules to reviewer panels, QA gates, and escalation processes. For practical guidance on oversight workflows, records, and change control, see Operationalizing Human Oversight, Records, and Change Control for Enterprise Voice AI (https://blog.peakdemand.ca/post/operationalizing-human-oversight-records-change-control-voice-ai).
- Define reviewer quotas, sampling methodologies, and remediation SLAs.
- Integrate QA findings into prioritized engineering and training backlogs.
- Ensure handoff evidence is stored with session records for future audits.
Data strategy, security and jurisdictional boundaries
Voice AI introduces layered data flows and subprocessors. Procurement must treat residency, transfer mechanisms, subprocessors, and access policies as first‑class contract terms.
Residency, transfers, and subprocessors
Document hosting regions, backup geography, remote‑support access, and intended subprocessors in the contract. Specify the legal mechanism for cross‑border transfers (standard contractual clauses, adequacy decisions, etc.) as applicable in your jurisdiction and confirm obligations with qualified counsel. Keep in mind that operational needs such as remote debugging or vendor support can create cross‑border access even if primary hosting remains in a specified region.
- List hosting and backup regions, and define acceptable subprocessors with notification and objection rights.
- Require explicit descriptions of remote‑support access methods (bastion hosts, VPN, remote session logs).
- Include data export and deletion obligations for offboarding.
Recording, retention and privacy controls
Define what categories of voice data are recorded (full audio, transcripts, PII), retention periods, and anonymization/pseudonymization treatments. Apply consent and notification controls appropriate to the jurisdiction. For high‑sensitivity data, require in‑scope encryption, minimal access principles, and hardened storage with separate key custody when needed.
- Define precise retention schedules and deletion verification processes.
- Partition PII and sensitive transcripts from analytics stores, and use tokenization when possible.
- Require breach notification processes and timelines in vendor contracts; confirm local obligations with counsel.
Security controls and operational access
Secure the entire call flow: session tokens, TLS in transit, envelope encryption for stored artifacts, and role‑based access controls for operational tooling. Define emergency access, audit trails for operator actions, and least‑privilege policies for adapters and orchestration components.
- Require multi‑factor authentication and fine‑grained role separation for production access.
- Log operator actions and provide immutable activity streams for audits.
- Contractually enforce vulnerability‑fix timelines and pen‑test obligations.
Procurement checklist and vendor evaluation
Translate architecture and governance requirements into procurement artifacts: RFP sections, SOWs, acceptance tests, and operational readiness gates.
Contract structure and SOW essentials
Include a clear responsibilities matrix (RACI), SOW deliverables for adapters and orchestration, acceptance criteria with test harnesses, and an exit/transition plan. Require change‑control and software lifecycle commitments (maintenance windows, patch cadence).
- Demand test harnesses that exercise adapter contracts and failure modes.
- Make observability and audit log exports contractual deliverables.
- Include forensic support and evidence preservation clauses for incidents.
Proofs, acceptance tests and exit planning
Acceptance should be based on business outcomes and technical verification: run pilot scenarios that measure containment, false escalations, latency, and adapter error handling. Define a transition plan that includes code, documentation, and exportable configuration so the enterprise is not operationally locked in.
- Use staged acceptance: sandbox verification, pilot with controlled traffic, and production ramp.
- Specify export formats for rules, prompts, and configuration to enable portability.
- Include financial and operational remedies tied to missed SLAs and data obligations.
Vendor due diligence and references
Ask vendors for runbooks, observability screenshots, evidence of adapter maintenance, and post‑incident reviews. Evaluate their QA processes and sample audit logs. Review third‑party subprocessors and verify contractual commitments for security and breach response.
- Request documented QA sampling methodology and results.
- Review audit logs sample extracts to validate observability claims.
- Require the right to audit or attestations for subprocessors.
Related Peak Demand resources
Industry and AI sources reviewed
- Artificial Intelligence Risk Management Framework (AI RMF 1.0)National Institute of Standards and Technology (NIST)
- AI Risk Management Framework: Generative AI ProfileNational Institute of Standards and Technology (NIST)
- OECD AI PrinciplesOrganisation for Economic Co-operation and Development
Privacy, telecommunications, recording-consent, cybersecurity, consumer-protection, employment, and records obligations vary by jurisdiction and use case. This article is operational guidance, not legal advice; organizations should confirm applicable requirements with qualified professionals.
Frequently asked questions
A serious managed service should include discovery, workflow design, telephony, integrations, validation rules, testing, monitoring, human escalation, incident handling, change control, analytics, and ongoing optimization. The value is the complete operating system around the model, not access to a model alone.
Official reference: Artificial Intelligence Risk Management Framework (AI RMF 1.0)
The operating model should assign clear owners for telephony, prompts, knowledge, APIs, credentials, incident response, analytics, approvals, and release management. Enterprise buyers should avoid deployments where those responsibilities are ambiguous or split across vendors without accountability.
Official reference: Artificial Intelligence Risk Management Framework (AI RMF 1.0)
Evaluate the complete workflow under realistic volume, latency, interruption, transfer, integration, and failure conditions. Measure task completion, escalation quality, unsupported responses, system errors, recovery behavior, and how quickly operators can detect and correct problems.
Official reference: Artificial Intelligence Risk Management Framework (AI RMF 1.0)
Ask for documented use-case boundaries, data handling, access controls, model and prompt change management, evaluation procedures, audit logs, human-oversight rules, incident response, subcontractor dependencies, and a process for reviewing material system changes.
Official reference: Artificial Intelligence Risk Management Framework (AI RMF 1.0)
Need deeper enterprise Voice AI integration?
For custom APIs, SIP and telephony architecture, multi-system workflows, QA, observability, and enterprise deployment, Peak Demand commonly evaluates platforms such as Retell AI as part of a managed architecture.
Explore Retell for Enterprise Voice AIPeak Demand may earn a commission from this link.


