Utility Data Mesh and Domain Governance for Predictive Voice AI Operations
A practical operating framework for utilities deploying high-volume Voice AI for customer service and outage communications. Covers data mesh design, domain governance, validated integrations, escalation controls, and measurable outcomes for safe, reliable operations.
1. Why a Data Mesh for Voice AI in Utilities
Voice AI for utilities touches multiple operational domains and systems. A data mesh decouples ownership while creating interoperable, governed data products that Voice AI can safely query and act on.
Decentralized ownership, centralized contracts
Utilities are organized by function: customer service, outage management, field operations, billing, and regulatory reporting. Implement a domain-aligned data mesh where each team owns data products (for example: Customer Account Product, Premise Topology Product, Outage Event Product). Ownership includes schema, SLAs, retention, and an approved adapter surface. Enforce data contracts (schema, events, permitted operations) to remove ambiguity between Voice AI consumers and operational sources.
- Assign a product owner and steward for each domain product.
- Version data contracts and require backward-compatible changes or controlled migration windows.
- Publish a catalogue of approved adapters and allowed API methods per product.
Why this matters for outage communications
During outages, callers expect accurate status and realistic ETAs. A data mesh prevents stale or conflicting data by ensuring Voice AI queries a maintained Outage Event Product backed by the OMS or NOC. For service-requests, the Voice AI should write only via an approved Service-Request Product adapter that enforces validation rules and creates auditable tickets.
- Voice AI reads status and metadata from the Outage Event Product, not cached transcripts.
- Writes for work orders or move requests go through validated business adapters that apply business rules and return ticket IDs.
2. Domain Governance: Policies, Roles, and Failure Boundaries
Domain governance converts the catalogue and contracts into operational constraints: who may access what, what the Voice AI can say or do, and how failures escalate.
Policy primitives and role definition
Create domain-level policies that include permitted read scopes, approved write operations, authentication modes, and telemetry requirements. Define roles for data product owners, integration engineers, Voice AI flow owners, contact-centre supervisors, and incident commanders. Each role has change controls and emergency override rules.
- Minimum necessary access: grant read-only or limited write rights to Voice AI adapters.
- Change gates: require cross-domain review for any schema or adapter change affecting outage or safety-related products.
- Emergency freeze: a documented process to stop automated write actions and force human-only intake.
Failure boundaries and human-in-the-loop
Define deterministic failure modes: soft failures (temporary upstream API latency), hard failures (malformed responses), and safety failures (ambiguous caller claims about hazards). For each mode, specify whether the Voice AI will retry, respond with a safe message, or transfer to a human. Ensure human handlers receive the full event context and confidence signals to continue the interaction without re-collecting data.
- Soft failure: return earliest-authoritative status and include a timestamped certainty flag.
- Hard failure: open a monitored service ticket and transfer caller to a live agent.
- Safety failure: immediate escalation with audible confirmation that a human is connecting.
3. Integration Patterns: Approved Adapters and Account Validation
Reliable, secure integrations are the spine of Voice AI operations. Use controlled adapters for OMS, CIS/CRM, field dispatch, and meter topology. Keep lookups authoritative, and limit writes to validated endpoints.
Adapter model and approved API surface
Adopt a thin adapter layer that mediates between the Voice AI orchestration and backend systems. Adapters encapsulate auth, rate limiting, schema translation, and logging. Maintain an allowlist of adapter endpoints and a denylist for direct system access. Record adapter metadata in the data product catalogue so Voice AI chooses only approved endpoints.
- Adapters must authenticate using service credentials scoped to the minimal privilege.
- Adapters implement circuit-breaker logic and graceful degradation to cached status when permitted.
- Audit logs at adapter level for every read and write call, including caller ID, timestamps, and correlation IDs.
Account and premise validation workflow
Design a deterministic validation sequence: confirm caller identity through low-friction checks (account number partial, registered phone, service address), then confirm premise topology if required for outage correlation. If validation fails, default to a read-only status response or transfer to human verification. Never allow unvalidated callers to perform critical writes such as remote disconnects or safety-related work orders.
- Validation steps must be auditable and produce a validation score appended to the interaction record.
- For partial validation, permit information disclosure limited to non-sensitive status messages.
- For write operations, require multi-factor validation or a human confirmation step.
4. Operational Workflows and Escalation Controls
Translate the architecture into repeatable workflows that agents and field staff can trust during normal operations and incidents.
Standard call-to-action architecture
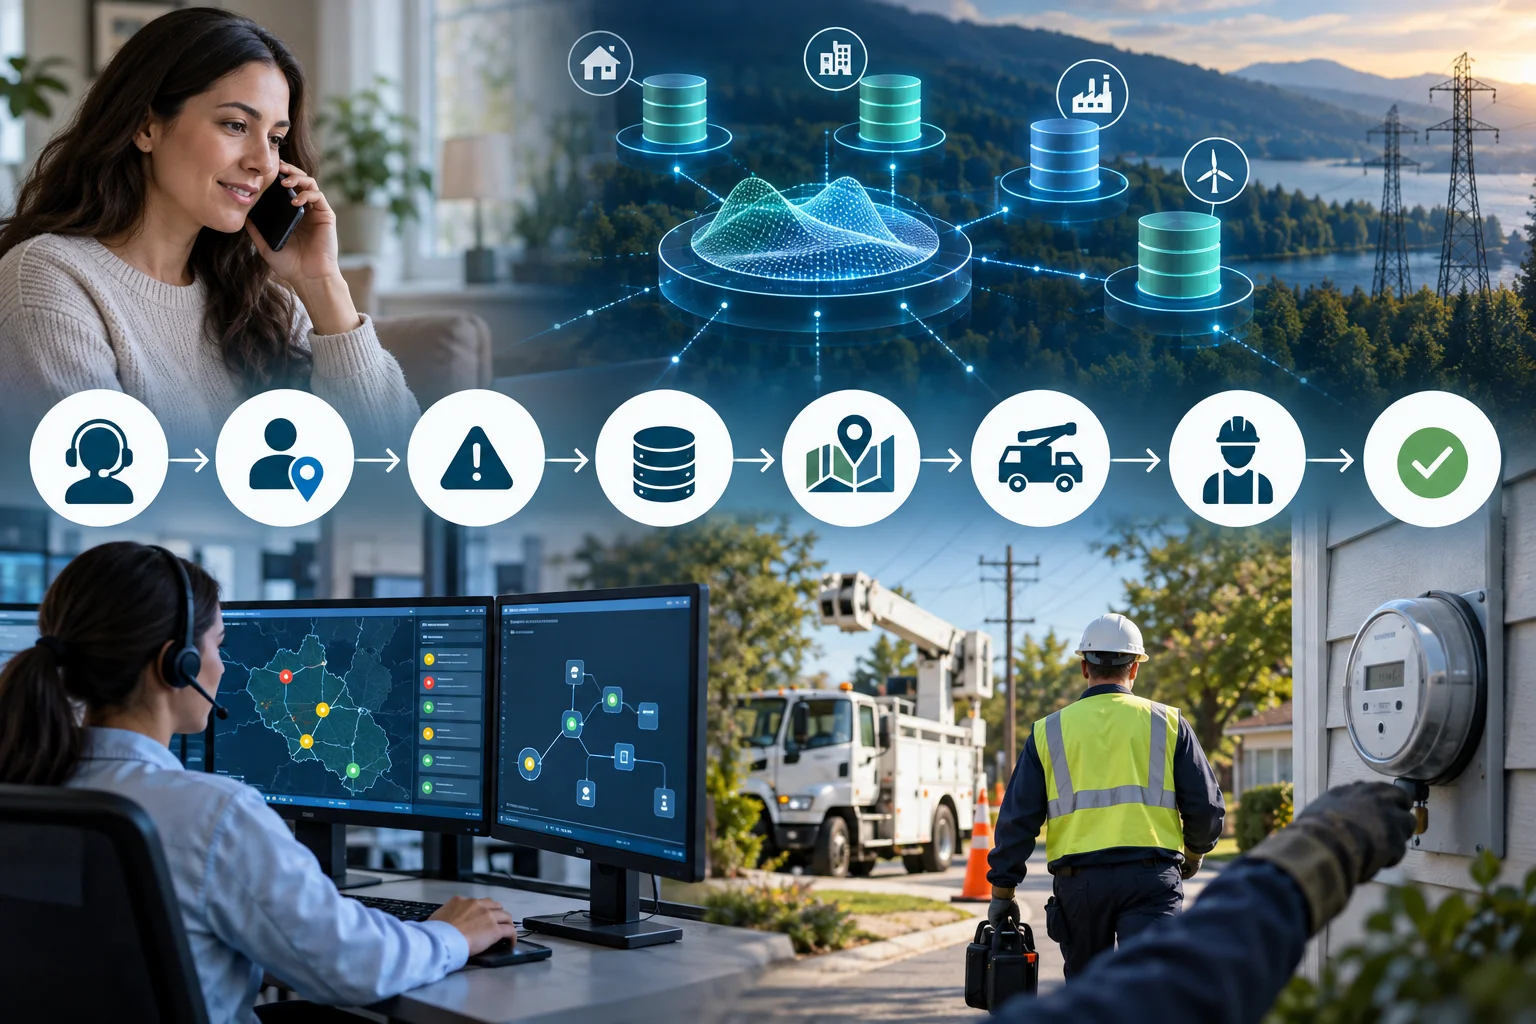
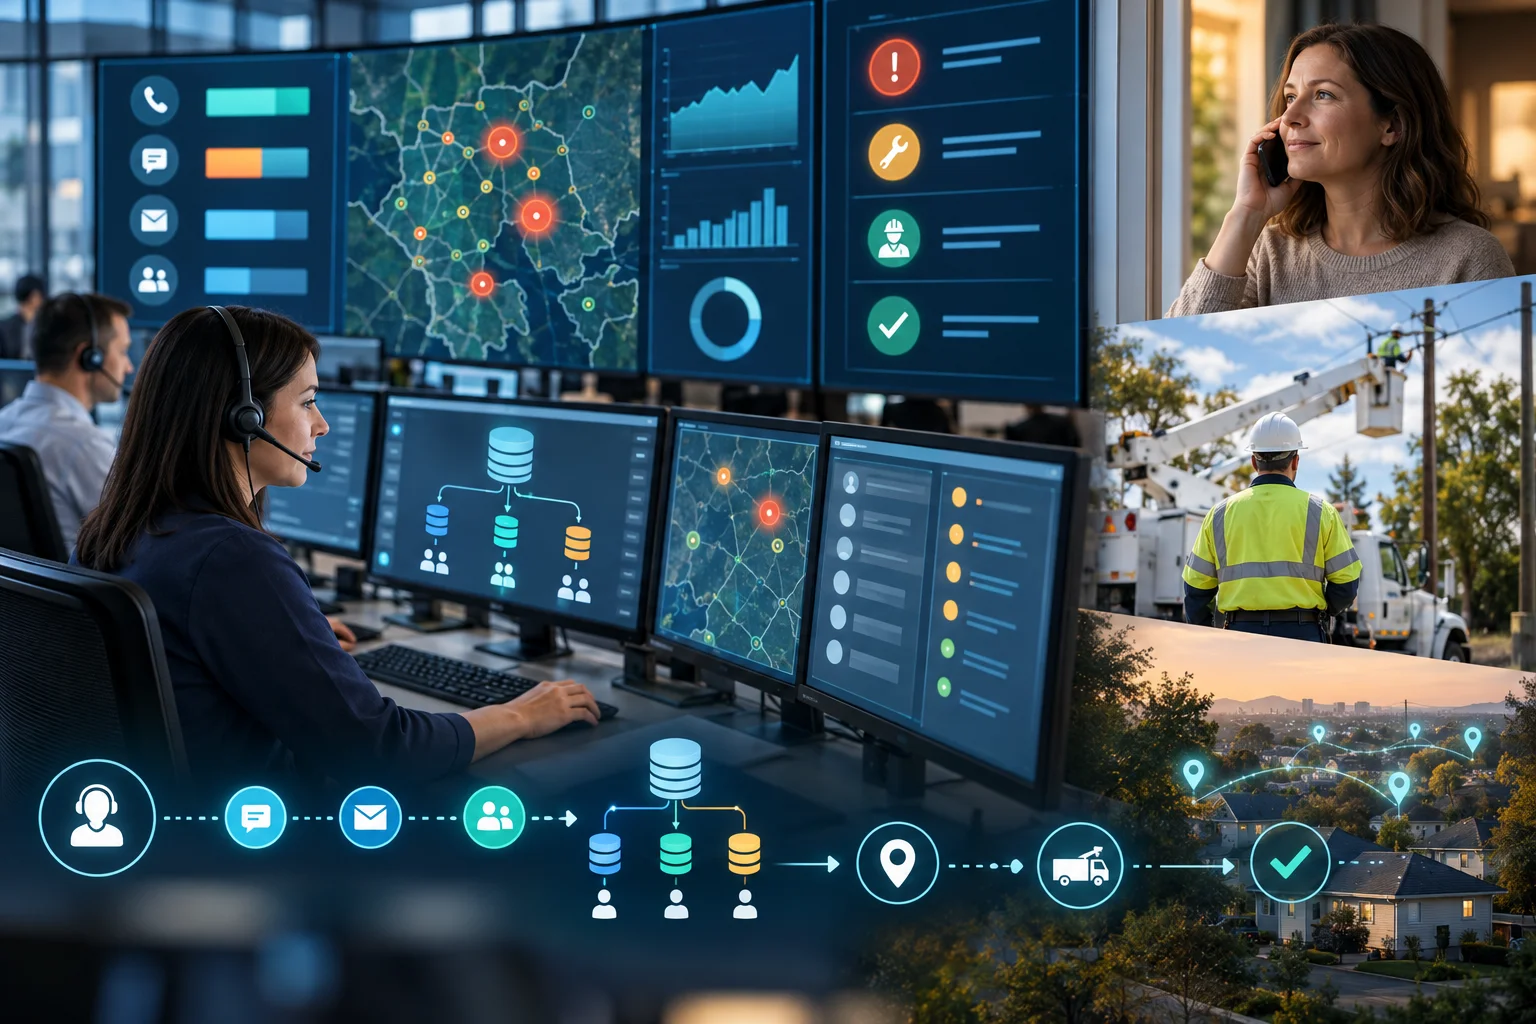
Keep the architecture explicit in playbooks: Customer call → Voice AI intake → account/premise validation → approved API or knowledge-source lookup → return status or create service request via adapter → present confirmation and ticket ID → store event and analytics. This flow preserves auditability and ensures no hidden side effects.
- Include correlation IDs at each step to link telephony, Voice AI transcript, adapter calls, and resultant tickets.
- Ensure transcripts and decisions are retained according to the domain retention policy.
- Provide agents with an interaction summary and audit trail when escalation occurs.
Escalation tiers and handoff fidelity
Define escalation tiers: Tier 0 (self-serve automated containment), Tier 1 (live contact-centre agent), Tier 2 (operational command/unit), Tier 3 (field emergency response). For each handoff, pass structured context: validation state, confidence scores, queries performed, and adapter responses. Handovers should avoid repeat verification where permitted by policy.
- Automated handoffs should pre-populate agent desktops with structured data and recommended next actions.
- Escalation triggers include confidence thresholds, safety keywords, and critical-system write attempts.
- Test handoffs in simulated surge scenarios to validate handoff latency and information completeness.
5. Cybersecurity and Resilience Controls
Protect Voice AI operations with controls that span identity, segregation, logging, and maturity alignment to recognized models.
Technical controls and segregation
Segment Voice AI adapters from core OT and control networks. Enforce network segmentation, mutual TLS, principle-of-least-privilege credentials, and strict logging. Apply read/write separation where possible and require multi-party confirmation for any action that could materially affect service or safety.
- Network segmentation between customer-facing adapters and operational control networks.
- Strong identity for service accounts with short-lived credentials and recorded key rotation.
- Full request/response logging with retention aligned to domain policy.
Resilience, incident response, and testing
Plan for surge, integration failures, and compromise scenarios. Exercise incident response plans, include Voice AI-specific playbooks, and maintain a business-continuity path that routes callers to human agents if automation is degraded. Document backup geography, subprocessors, remote-support access, and cross-border transfer constraints where they affect data residency.
- Maintain a service-level contingency that includes human fallback capacity for peak outage periods.
- Define backup hosting region, subprocessors, and remote-support vendor access in procurement documents.
- Run regular tabletop and live tests that include simulated adapter failure and large-scale surge.
6. Measurement, Procurement, and Operational Outcomes
Define the metrics and procurement evidence that demonstrate operational readiness and governance maturity.
Key operational metrics
Measure containment (percent of calls fully served by Voice AI), escalation fidelity (correct escalations vs false escalations), validation accuracy, ticket creation accuracy (writes that meet business rules), and time-to-resolution for escalated events. Use event-level analytics and correlated telemetry to detect drift and to feed governance reviews.
- Containment rate, escalation precision and recall, and first-contact resolution for agent-handled escalations.
- Adapter success rate, mean latency, and percent of calls hitting cached vs authoritative data.
- Audit coverage: percent of interactions with complete logs, correlation IDs, and retention compliance.
Procurement checklist for vendors
Require vendors to demonstrate: adapter-level logging, integration test evidence, role-based access control, data residency and subprocessors disclosure, surge capacity plans, and a transparent escalation and incident response playbook. Validate these claims with tabletop tests and operational acceptance tests before any production cutover.
- Ask for documented adapters, test harnesses, and a list of supported backend systems.
- Require proof of role-based access and ability to freeze automated writes.
- Include contractual requirements for telemetry access and periodic QA sampling.
7. Operating Safely at Scale: Practical Next Steps
Convert strategy into a phased program aligned with risk and operational priority.
Phase 1: Domain product foundation
Start by defining 3–4 domain products (Customer Account, Premise Topology, Outage Event, Service Request) with owners, contracts, and adapters. Implement one end-to-end Voice AI workflow for a low-risk use-case (status queries) as a proof of safe integration.
- Publish data contracts and an adapter allowlist before Voice AI consumes the product.
- Run a pilot focused on read-only outage status responses with QA sampling.
Phase 2: Controlled write and escalation
Introduce validated write paths for service requests and non-safety field scheduling after controlled acceptance tests. Expand validation rules and human-in-the-loop policies and start regular governance reviews using event-level analytics.
- Authorize write actions only via adapter endpoints that perform business-rule validation.
- Institute weekly QA and monthly governance reviews combining telemetry and human audits.
Related Peak Demand resources
Industry and AI sources reviewed
- AI Risk Management Framework — Critical Infrastructure ProfileNational Institute of Standards and Technology (NIST)
- Cross-Sector Cybersecurity Performance GoalsCybersecurity and Infrastructure Security Agency (CISA)
- Cybersecurity Capability Maturity Model (C2M2)U.S. Department of Energy
Utility cybersecurity, critical-infrastructure, records, customer-protection, and emergency-communications obligations vary by jurisdiction and service type. This article is operational guidance, not legal advice; organizations should confirm applicable requirements with qualified professionals.
Frequently asked questions
Good starting points include billing and account questions, move-in or move-out intake, appointment scheduling, service-request capture, outage-status messaging from approved systems, payment-routing assistance, and structured escalation. Safety-critical and infrastructure-control decisions should remain with qualified utility teams.
Official reference: Cross-Sector Cybersecurity Performance Goals
Use the minimum approved identifiers needed for the workflow, validate them against the utility's system of record, limit data exposure, and provide a human-assisted path when verification fails. The Voice AI should not guess account, premise, or outage information.
Official reference: Cross-Sector Cybersecurity Performance Goals
Use controlled adapters, strict schemas, timeouts, retries, audit logs, safe failure states, and human escalation. The system should distinguish approved utility data from model-generated language and should never present stale or unverified operational information as fact.
Official reference: Cybersecurity Capability Maturity Model (C2M2)
Track containment by request type, successful validations, transfers, abandoned calls, integration errors, incorrect or stale responses, time to resolution, customer follow-up, and the percentage of cases completed safely without manual rework.
Official reference: Cybersecurity Capability Maturity Model (C2M2)
Build resilient utility customer-service automation
Peak Demand helps utilities connect Voice AI to approved customer-information, outage-communication, service-request, dispatch, escalation, and analytics workflows.
Schedule a discovery call


