Cross-Channel Identity & Session Continuity for Enterprise Voice AI
Practical architecture and procurement guidance for designing reliable cross-channel identity and session continuity in enterprise Voice AI. Covers integration patterns, decision boundaries, managed‑service scopes, governance controls, observability, and vendor evaluation.
1. Why cross‑channel identity and session continuity matter
Enterprise voice channels remain critical for high‑value interactions. Customers move between IVR, web chat, mobile app callbacks, and live agents; continuity in identity and session context is essential to reduce friction, lower resolution time, and maintain compliance boundaries. This section explains the operational value and the buyer questions to resolve before procurement.
Operational benefits and measurable outcomes
Continuity reduces repeat authentication steps, shortens call handle time, and improves first‑contact resolution. For procurement and architecture teams, measurable outcomes should include session continuity rate (percentage of interactions with preserved context), mean time to human handoff, re‑authentication frequency, and downstream error rates attributable to identity mismatches. Specify baseline and target metrics in SLOs to make vendor proposals comparable.
- Session continuity rate — target and measurement window
- Mean time to human handoff when continuity fails
- Authentication re‑prompts per session (ideally minimized with secure linking)
- Error-rate attribution to identity resolution failures
Procurement decisions this drives
Decide early whether the vendor provides full integration ownership or only a managed Voice AI component. Ownership choices change risk allocation: full integration implies vendor responsibility for adapters to CRM/CIS/ERP and for maintaining mapping logic; component‑only implies internal teams manage integration and policy. Insist on clear handoff points, documented interfaces, and runbooks that define expected behavior under failure.
- Integration ownership: vendor‑owned adapters vs buyer‑owned adapters
- Operational handoffs and escalation routes documented in runbooks
- Service acceptance tests for continuity across channels
2. Reference architecture and key components
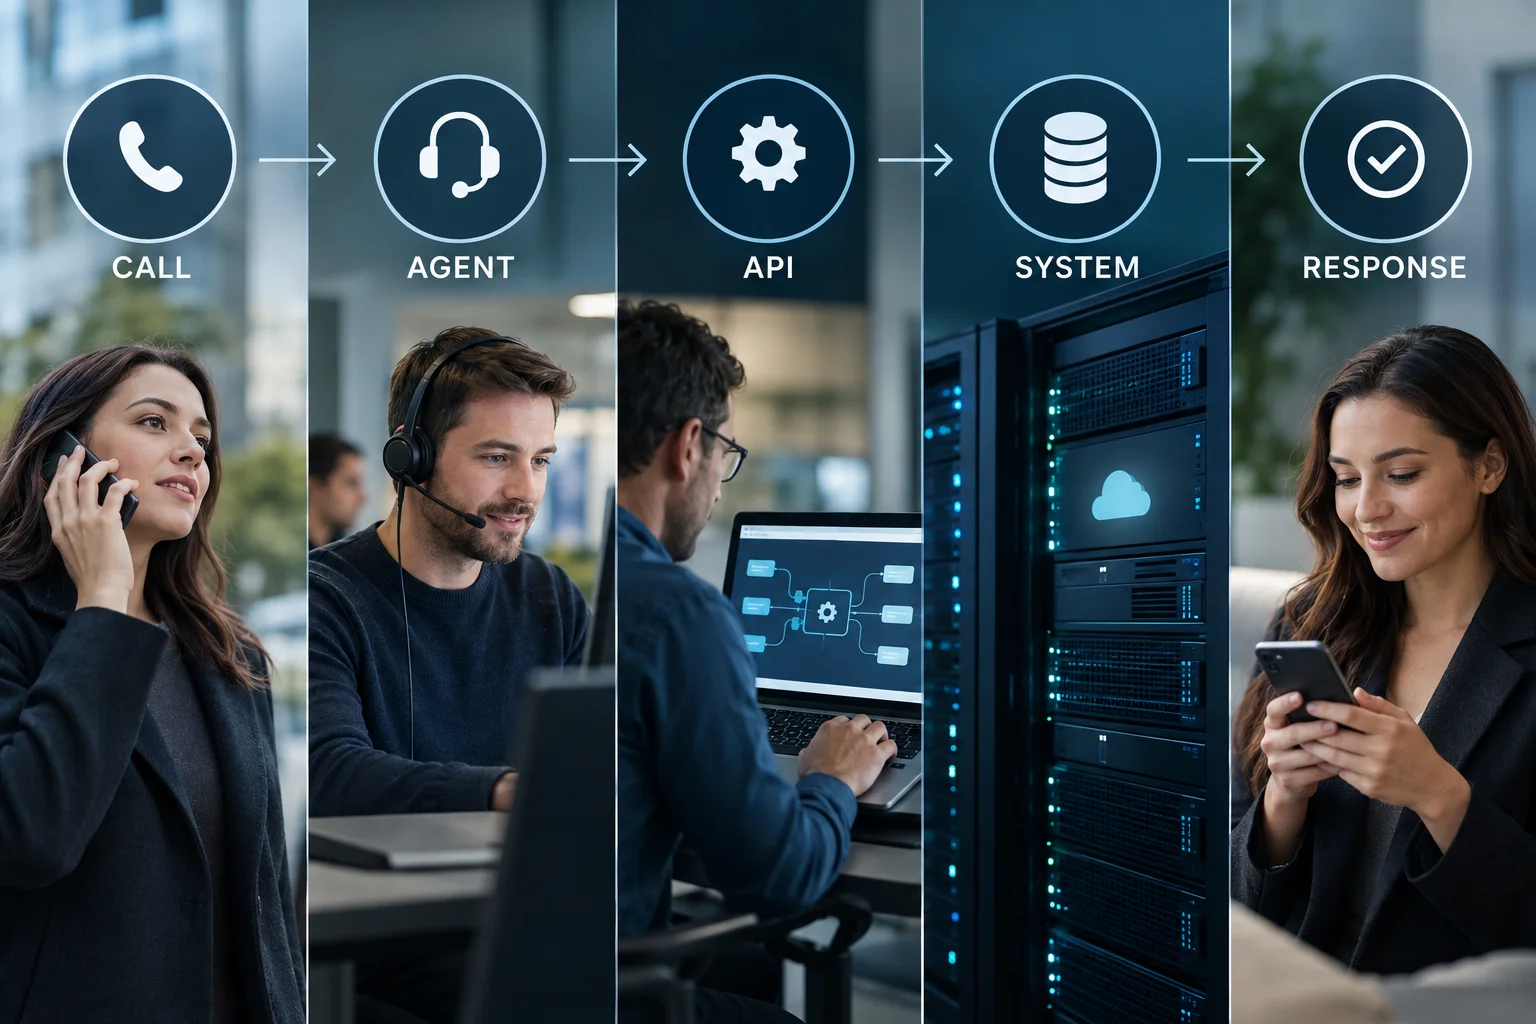
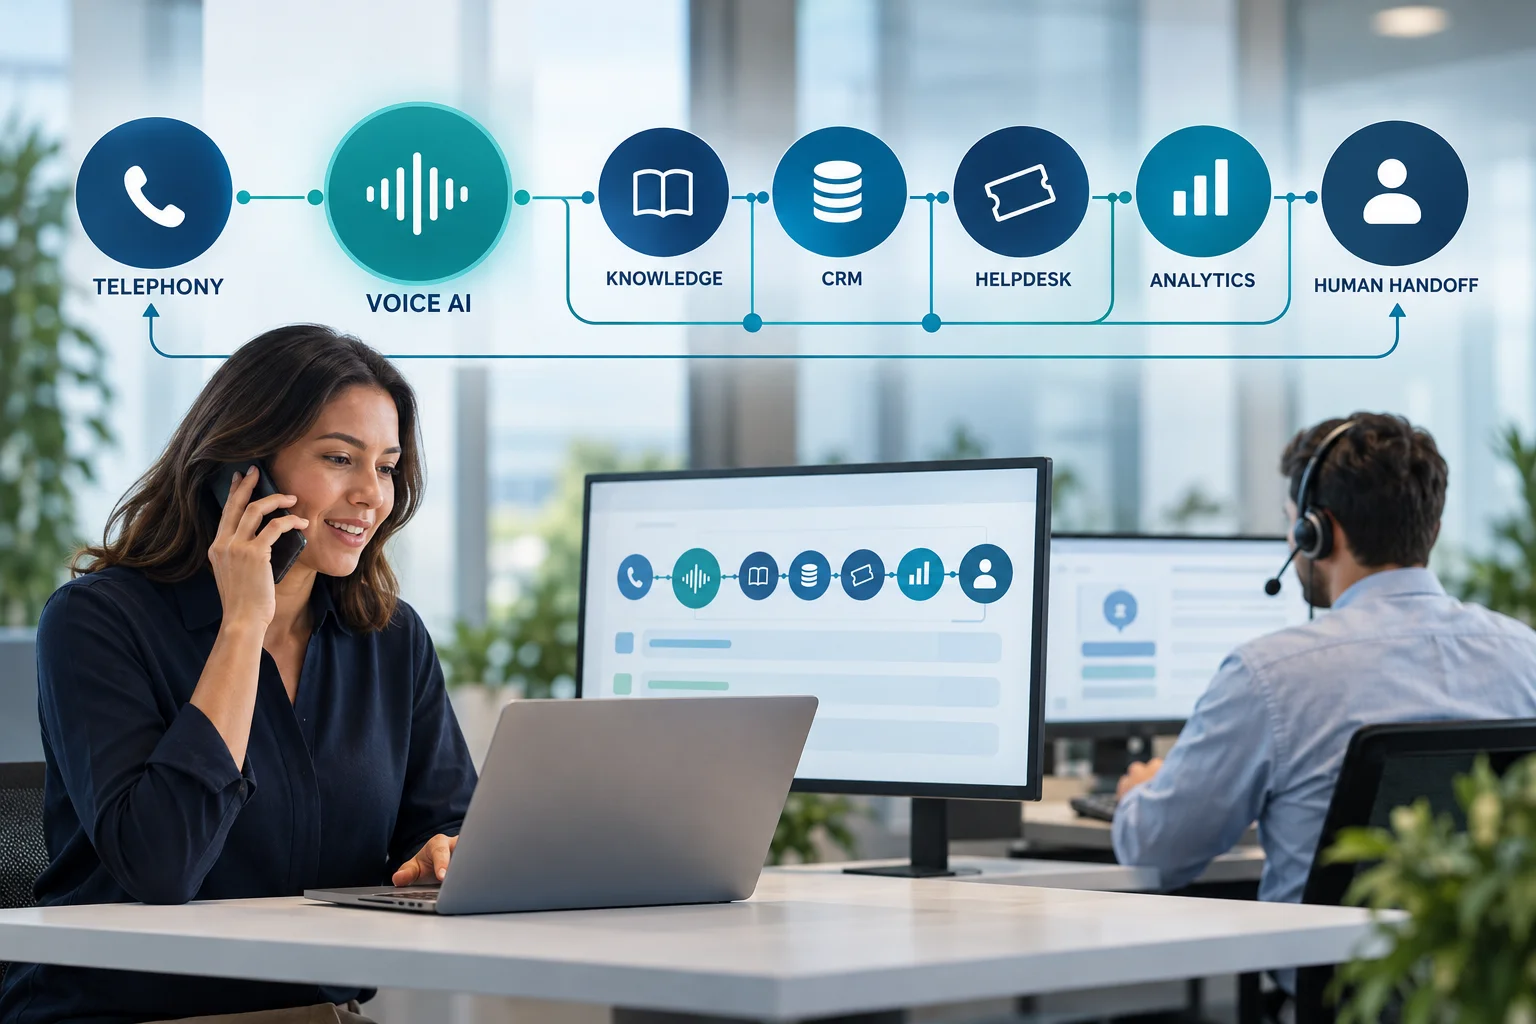
A durable design separates conversational models from decisioning and enterprise systems. Use the canonical flow: Caller → Voice AI → business‑rules layer → approved enterprise systems → response/transaction/human handoff → QA & analytics. Below are component responsibilities and integration patterns.
Core components and responsibilities
Voice AI handles speech capture, ASR, NLU, prompt management, and local session context (recent utterances, session tokens). The business‑rules layer owns identity resolution, entitlements, fraud checks, authorization, and orchestration of side effects. Approved enterprise systems (CRM, billing, order management, KYC platforms) are authoritative sources of record. QA and analytics capture call traces, decision logs, and human‑in‑the‑loop actions for continuous improvement.
- Voice AI: session token issuance, ephemeral context, local NLU state
- Business‑rules layer: identity resolution, entitlements, orchestration
- Approved enterprise systems: authoritative data via controlled adapters
- QA & analytics: auditable traces, recording indices, error tagging
Integration patterns and adapters
Integrations must be explicit and auditable. Use controlled adapters (API gateways, secure connectors) between the business‑rules layer and enterprise systems. Implement idempotent operations and compensating transactions to manage partial failures. For external or third‑party subprocessors, document subprocessors, transfer mechanisms, and data residency. Ensure adapters support both synchronous lookups and asynchronous reconciliation to reduce latency and avoid blocking critical conversations.
- Synchronous lookups for real‑time validation (eligibility, balance)
- Asynchronous reconciliation for non‑blocking updates (post‑call records)
- Idempotency keys and compensating transactions for partial failures
- Document subprocessors, hosting regions, and support access
3. Identity linking and session stitching methods
Stitching sessions across channels requires a mix of deterministic identifiers (explicit IDs and tokens) and probabilistic matching. Design for principled fallbacks, consent, and privacy considerations.
Deterministic linking: tokens, phone numbers, and account keys
Deterministic approaches are preferred where available. Examples: a secure session token passed between a mobile app and the Voice AI via DTMF or app‑initiated callback, authenticated account numbers matched to CRM records, or telephony identifiers (CLI/ANI) mapped to known accounts. Tokens should be short‑lived, scope‑restricted, and revocable. Architect token exchange as part of the business‑rules layer to centralize policy on retention, consent, and logging.
- Use ephemeral session tokens for direct app ↔ voice continuity
- Scope tokens to permissible actions and expiry windows
- Map CLI/ANI to verified accounts only after fraud checks
Probabilistic stitching and privacy trade‑offs
When deterministic identifiers are absent, probabilistic matching (voiceprint, behaviour signals, historical patterns) can improve continuity but introduces error and privacy risk. Define confidence thresholds, require step‑up authentication for high‑risk transactions, and log probabilistic matches with a justification field. Store only the minimal derived attributes needed for matching and ensure they are treated as sensitive data.
- Define confidence thresholds and explicit step‑up policies
- Keep probabilistic attributes minimised and auditable
- Avoid using high‑risk biometric matches without explicit consent and governance
Privacy, data residency, and consent
Document where voice recordings, session tokens, and derived identifiers reside (hosting region, backup region), and where subprocessors may access data. Provide clear consent and retention policies to callers, and distinguish between transient session data and long‑term analytics. Procurement should require vendors to disclose subprocessors, transfer mechanisms, retention durations, and breach notification processes so buyers can confirm obligations with legal counsel.
- Specify hosting region, backup region, and backup retention
- Require subprocessor disclosure and breach notification SLAs
- Define recording consent flows and retention semantics
4. Business‑rules layer, orchestration, and failure boundaries
The business‑rules layer is the linchpin: it resolves identity, enforces policies, and decides automation versus human escalation. Define explicit failure boundaries and safe fallbacks to manage risk.
Decision boundaries and risk controls
Codify which actions are safe to automate (balance inquiry, appointment scheduling) and which require human oversight (billing disputes, account closures). Embed rule versions, testing artifacts, and change‑control notes into the rules engine. For high‑risk classes, require explicit human approval workflows and ensure the system captures the approver identity and decision rationale in logs.
- Classify actions by risk and required assurance level
- Version rules and require staged rollout with QA gates
- Always log human approvals with identity and rationale
Fallbacks, compensations, and human handoff
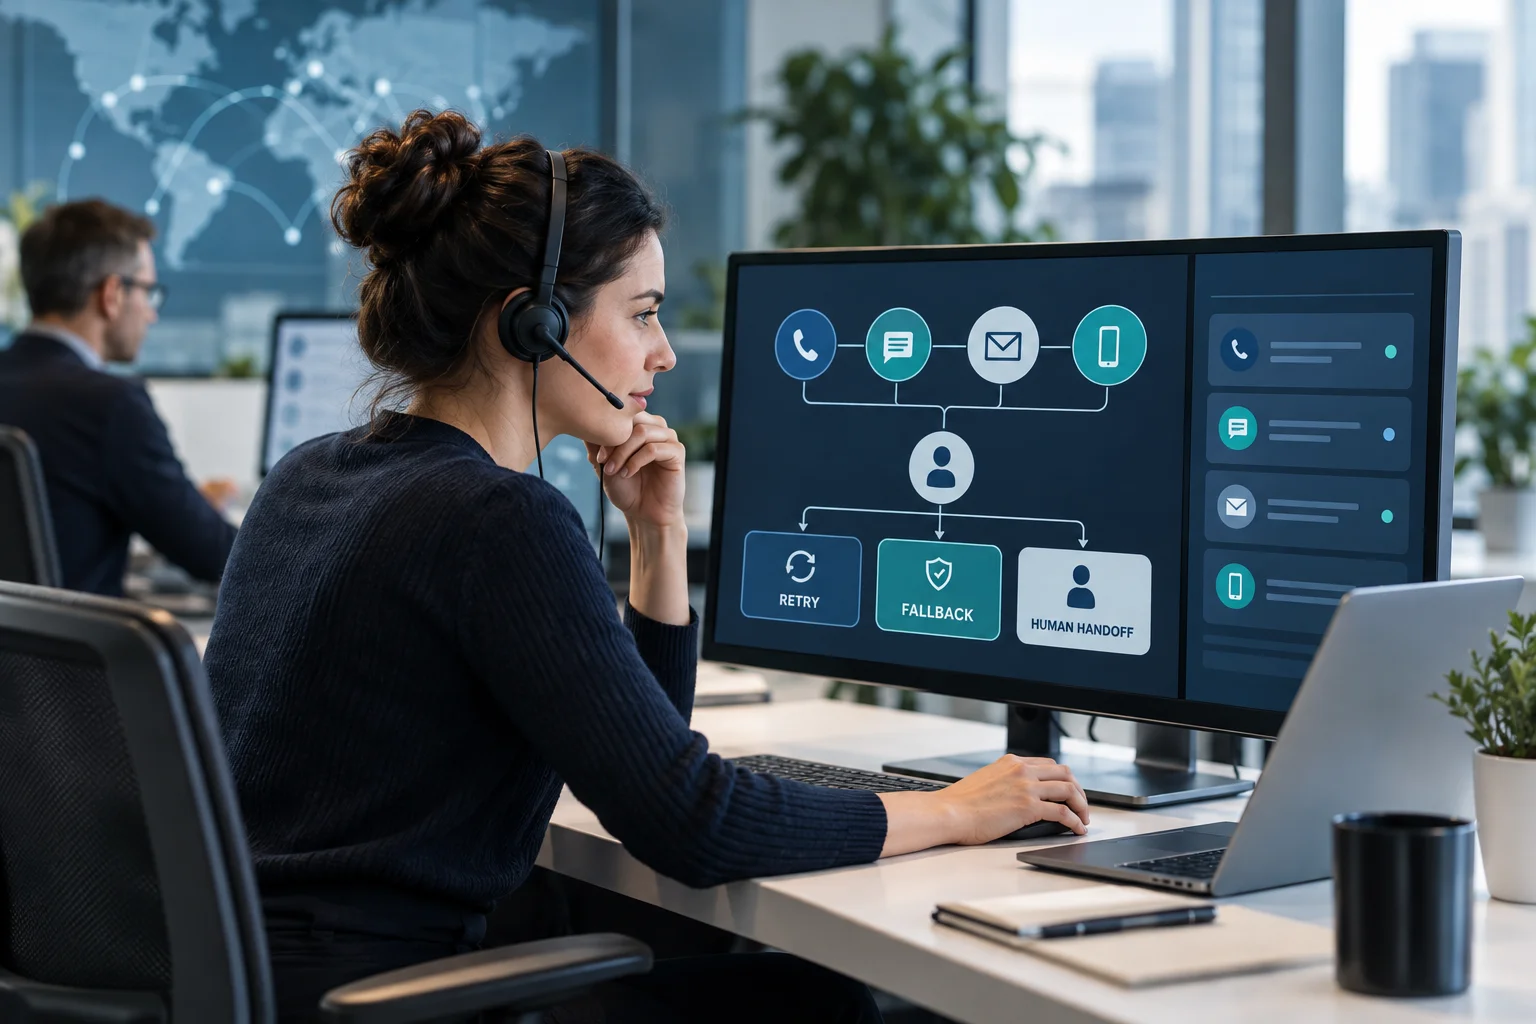
Design deterministic fallback steps when identity or system lookups fail: offer re‑authentication, fall back to partial service with clear disclosure, or perform an immediate human transfer. Compensating transactions must be available when a downstream write fails after a customer hearing an affirmative confirmation. All fallbacks should be documented in runbooks and included in vendor acceptance testing.
- Predefined fallback menus and re‑authentication paths
- Compensating transactions and rollbacks documented per transaction type
- Escalation playbooks for persistent failures
5. Managed services, ownership, SLAs and observability
Buyers must procure operational guarantees, not just software. Specify scope boundaries, SLOs, observability requirements, and continuous improvement expectations.
Defining managed‑service scope
A managed Voice AI service should describe components included: hosted Voice AI runtime, business‑rules engine, adapters it will maintain, QA and monitoring, human escalation staffing, and ongoing optimization cycles. Where buyers retain integrations, define APIs and test harnesses to enable parallel validation. Insist on documented onboarding tasks, maintenance windows, and runbooks for incident response.
- List adapters included and those out of scope
- Require runbooks, incident playbooks, and maintenance windows
- Define optimization cadence and who owns change control
SLOs, observability, and traceability
Specify SLOs that align to continuity metrics: session continuity rate, API latency for identity lookups, successful handoff percentage, and time to human answer. Require full traceability: per‑call traces that include prompts, decisions, identity resolution steps, and adapter responses. Demand dashboards and access to raw traces for internal auditors. For audit logging and traceability, see Peak Demand’s technical guidance on Voice AI audit logs.
- Session continuity rate and continuity SLO thresholds
- Per‑call trace export with decision timestamps and identifiers
- Uptime/latency SLOs for lookup APIs
Vendor responsibilities for QA and optimization
Vendors should provide test harnesses that simulate multi‑channel journeys, synthetic transactions for regression testing, and pre‑production environments with representative data masking. Require shared KPIs for continuous improvement and a defined change‑control board (CCB) process for updates to the rules engine and NLU models. Peak Demand’s managed service guidance outlines expectations buyers should codify in contracts.
- Pre‑prod test harness and synthetic multi‑channel journeys
- Change Control Board with staged rollout criteria
- Shared KPI dashboard and quarterly optimization plan
6. Governance, QA, auditability and human oversight
Rigorous governance ensures safety and traceability. Formalize policies for human oversight, records retention, change control, and auditability before deployment.
Human oversight and change control
Document which decisions require human intervention and how oversight is operationalized. Maintain auditable records of rule changes, model updates, and their acceptance tests. Ensure that human reviewers have access to context‑rich traces and that decisions are reversible where appropriate. The NIST AI Risk Management Framework and related generative AI guidance recommend explicit human oversight policies and change‑control artifacts for AI systems and are useful references when drafting governance.
- Define roles and responsibilities for approvers and reviewers
- Require traceable change logs with test evidence
- Operationalize human review with contextual traces
Audit trails, records, and retention
Audit trails must capture steps used to link identity and stitch sessions: token issuances, lookup responses, confidence scores, rule versions, and human approvals. Specify retention windows, anonymization requirements for analytics, and conditions for replayable traces for dispute resolution. For technical guidance on audit logs and traceability, consult Peak Demand’s Voice AI audit logs resource.
- Capture token events, lookup calls, and decision logs
- Define retention and anonymization for analytics datasets
- Provide replayable traces for dispute investigation
Testing and validation regimes
Require structured QA: unit tests for rules, integration tests for adapters, regression tests for NLU, and adversarial testing for identity spoofing. Include periodic red‑team exercises for fraud scenarios. Capture KPIs that drive go/no‑go for releases and require remediation plans for any release failing minimum continuity or safety thresholds.
- Unit, integration, regression and adversarial tests
- Release gating tied to continuity and safety KPIs
- Remediation plans and rollback criteria
Related Peak Demand resources
Industry and AI sources reviewed
- Artificial Intelligence Risk Management Framework (AI RMF 1.0)National Institute of Standards and Technology (NIST)
- OECD AI PrinciplesOrganisation for Economic Co-operation and Development
- AI Risk Management Framework: Generative AI ProfileNational Institute of Standards and Technology (NIST)
Privacy, telecommunications, recording-consent, cybersecurity, consumer-protection, employment, and records obligations vary by jurisdiction and use case. This article is operational guidance, not legal advice; organizations should confirm applicable requirements with qualified professionals.
Frequently asked questions
A serious managed service should include discovery, workflow design, telephony, integrations, validation rules, testing, monitoring, human escalation, incident handling, change control, analytics, and ongoing optimization. The value is the complete operating system around the model, not access to a model alone.
Official reference: Artificial Intelligence Risk Management Framework (AI RMF 1.0)
The operating model should assign clear owners for telephony, prompts, knowledge, APIs, credentials, incident response, analytics, approvals, and release management. Enterprise buyers should avoid deployments where those responsibilities are ambiguous or split across vendors without accountability.
Official reference: Artificial Intelligence Risk Management Framework (AI RMF 1.0)
Evaluate the complete workflow under realistic volume, latency, interruption, transfer, integration, and failure conditions. Measure task completion, escalation quality, unsupported responses, system errors, recovery behavior, and how quickly operators can detect and correct problems.
Official reference: Artificial Intelligence Risk Management Framework (AI RMF 1.0)
Ask for documented use-case boundaries, data handling, access controls, model and prompt change management, evaluation procedures, audit logs, human-oversight rules, incident response, subcontractor dependencies, and a process for reviewing material system changes.
Official reference: Artificial Intelligence Risk Management Framework (AI RMF 1.0)
Need deeper enterprise Voice AI integration?
For custom APIs, SIP and telephony architecture, multi-system workflows, QA, observability, and enterprise deployment, Peak Demand commonly evaluates platforms such as Retell AI as part of a managed architecture.
Explore Retell for Enterprise Voice AIPeak Demand may earn a commission from this link.


